AI Coding Live News

CrowdStrike Agrees to Acquire Fiddler and Dreadnode and Ships an AI Kill Switch, Bringing Agent Observability, Pre-Deployment AI Security Testing and Agent Termination Into Falcon

At Fal.Con Europe in Barcelona on November 3, CrowdStrike said it signed definitive agreements to acquire AI agent observability company Fiddler AI and automated AI security testing company Dreadnode, and launched an AI Kill Switch in Falcon Guardian that can terminate a misbehaving agent, block it from relaunching and cut its enterprise network access. Both deals are expected to close in CrowdStrike's fiscal Q4 FY27, with the products generally available that quarter. CrowdStrike did not disclose prices; CyberScoop, citing the Wall Street Journal, put Fiddler at about $400 million and Dreadnode at about $95 million.
CrowdStrike Agrees to Acquire Fiddler and Dreadnode and Ships an AI Kill Switch, Bringing Agent Observability, Pre-Deployment AI Security Testing and Agent Termination Into Falcon

Key Takeaways

  • Both acquisitions were announced the same day and are expected to close in CrowdStrike's fiscal Q4 FY27, paid mostly in cash plus some stock subject to vesting conditions.
  • CyberScoop, citing the Wall Street Journal, puts Fiddler at about $400 million and Dreadnode at about $95 million, roughly $495 million combined; CrowdStrike did not disclose the amounts.
  • Fiddler will be sold as Falcon Observe: pre-deployment evaluation, tracing of decisions and tool calls across the agent hierarchy, drift and hallucination detection, and evaluation costs cut by up to 98% using purpose-built models.
  • Dreadnode runs more than 100 known AI attack strategies (jailbreaks, prompt injection, multi-turn and agent-specific attacks) against models, agent reasoning loops, applications and MCP servers, mapping findings to OWASP LLM Top 10, OWASP Agentic ASI01-ASI10, MITRE ATLAS and NIST AI RMF.
  • The AI Kill Switch is available today: an authorized admin triggers it, the agent is stopped first at the Gateway (endpoint enforcement coming soon), blocked from relaunching and cut off from the network, with every action logged.
Read full story

CrowdStrike: China-nexus VAPOR PANDA used the ARTEX multi-agent framework, mainly on DeepSeek, against 200+ organizations in 11 days

CrowdStrike reported on Oct 29 that the China-nexus espionage group VAPOR PANDA, starting Oct 17, ran the open-source agentic intrusion framework ARTEX with DeepSeek plus a second, unconfirmed commercial LLM, hitting more than 200 organizations in at least 14 countries from a single controller over 11 days. Post-exploitation was confirmed at nine organizations, where the BLOODALCHEMY backdoor was deployed. Planning agents used about 1.4 billion input tokens in a single intrusion, and recovered transcripts show a human operator steering the agents in Chinese at key decision points.

Key Takeaways

  • Over 11 days from Oct 17, one ARTEX controller targeted 200+ organizations in at least 14 countries, including several foreign ministries, 19 US pharma, semiconductor, defense, nuclear and finance organizations, and telecoms in the US, Belgium and the Philippines (CrowdStrike report)
  • Post-exploitation was confirmed at 9 organizations, which received the BLOODALCHEMY backdoor; at least 12 more saw password spraying and credential scanning
  • DeepSeek was the main model, plus a subscription commercial LLM CrowdStrike could not confirm; planning agents used about 1.4 billion input tokens in one intrusion
  • Recovered transcripts show an operator issuing Chinese instructions tagged as human instructions, including an order to find Windows hosts without the Falcon sensor
  • CrowdStrike says this is separate from the Storm-0940 ARTEX activity reported by Microsoft, and judges China-nexus groups will highly likely keep adopting such agent frameworks over the next 12 months
Read full story
Linked Models & Agents:

CrowdStrike: attacker used open-source AI pentest agent ARTEX plus Claude Code to breach South Korean financial firms

CrowdStrike Intelligence found Claude Code session histories, ARTEX configs and a CLAUDE.md in attacker open directories, showing a likely Chinese-speaking, financially motivated actor used the China-built open-source agentic pentest framework ARTEX (DeepSeek v4.1-flash primary, plus GLM-5.3 and Grok 4.6) to breach loan-inquiry and employee mobile systems at South Korean financial institutions from late September to early October 2026.

Key Takeaways

  • Window: late Sep to early Oct 2026; CrowdStrike attribution is moderate confidence, no named adversary
  • Model stack: DeepSeek v4.1-flash as ARTEX primary backend via likely reseller xcai[.]pro; GLM-5.3 and Grok 4.6 in Claude Code sessions
  • IOCs: 1 actor-controlled IP (38.244.50[.]120) plus 9 proxy IPs, with MITRE ATT&CK mapping
  • Reported impact: Shinhan 25,729 customers, Hana 89, Yegaram ~40,000 (press reports)
  • The upstream Autumn-27/ARTEX GitHub repo now returns 404
Read full story

Anthropic Cyber Mission: free OSS Scanner reports 77 critical and 803 high findings in its first week, plus Critical Infrastructure Defense with 11 partners

On Oct 8 Anthropic launched the Cyber Mission: (1) free opt-in OSS Scanner for critical open-source projects using strongest models including Claude Mythos, with PoC/explanation/candidate patches and >90% expected true-positive rate, no human triage; (2) Critical Infrastructure Defense Program with 11 founding partners including CrowdStrike, Palo Alto, Dragos, and Rockwell. Project Glasswing has surfaced 29,000+ candidate vulns. Oct 19 update: first scans have reported 77 critical and 803 high model-rated findings to maintainers; curl 8.23.0's high-severity HTTP/2 use-after-free CVE-2026-92392 was found by an early version.

Key Takeaways

  • Two tracks: free opt-in OSS Scanner (model-only reports) + Critical Infrastructure Defense Program (OT/power/water/transport; 11 founding partners)
  • Glasswing legacy: 29,000+ candidate vulns, ~6,000 human-triaged; ~5,000 reports sent when maintainers asked for bulk
  • Quality bar: 88% of 97 critical/high samples met CVD bar; expected true-positive >90% (no human review; severity can be off)
  • Enroll: core maintainers PR into Anthropic’s enrollment repo; also Claude for OSS free Max + Cyber Verification Program
  • First week (vendor-reported, model-rated, unreviewed): 77 critical and 803 high findings sent to maintainers; curl 8.23.0 fixed CVE-2026-92392 (HTTP/2 upload use-after-free, 8.12.0–8.22.0) found by an early version
Read full story
ADSponsored

Anthropic launches Claude Marketplace: 2,000+ connectors; spend commit on Cursor and partner agents

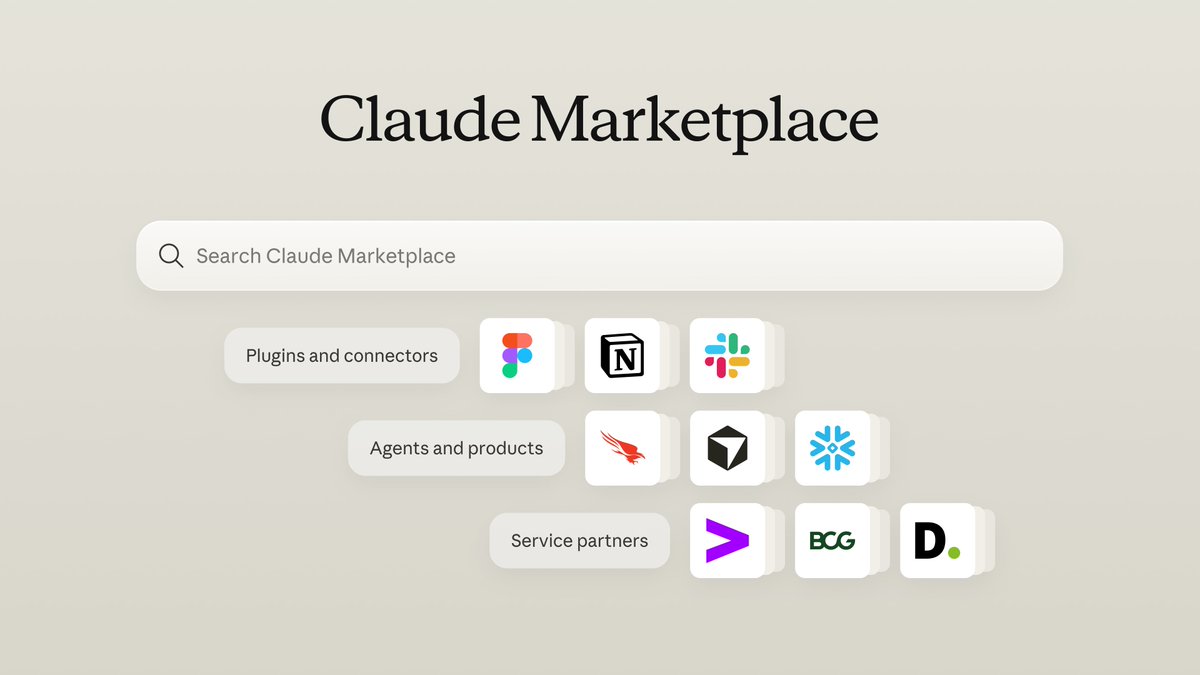
Claude (@claudeai) launched Claude Marketplace—one place for connectors/plugins, agents/products, and service partners. Customers get 2,000+ connectors (Atlassian, Google, Microsoft, Notion, Salesforce, …), can apply Anthropic committed spend to Claude-powered software from CrowdStrike, Cursor, Harvey, Legora, Lovable, Snowflake, and engage Accenture/BCG/Deloitte-style partners. Builders can list to reach Claude teams.

Anthropic launches Claude Marketplace: 2,000+ connectors; spend commit on Cursor and partner agents

Key Takeaways

  • Announcement: three shelves—connectors/plugins, agents/products, service partners.
  • Over 2,000 connectors/plugins (Google Drive, Gmail, Microsoft 365, Notion, Figma, Slack, …).
  • Apply Anthropic committed spend to partner software like CrowdStrike, Cursor, Harvey, Legora, Lovable, Snowflake.
  • Service partners via Claude Partner Network (Accenture, BCG, Deloitte); builders can apply to list.
Read full story

Claude Marketplace adds CrowdStrike, Cursor, Factory, Gamma, Vercel — buy with Anthropic spend commitment

Anthropic announced new Claude Marketplace listings: CrowdStrike, Cursor, FactoryAI, Gamma, and Vercel. Enterprises can apply Anthropic spend commitments toward more Claude-powered products and agents.

Key Takeaways

  • New listings: CrowdStrike, Cursor, FactoryAI, Gamma, Vercel.
  • Enterprises can spend Anthropic commitments on Claude-powered products/agents.
  • Start at claude.com/platform/marketplace.
Read full story