Vercel Security Review Enters Public Beta: Vulnerability Review on Every GitHub Push, One-Click Fixes with Vercel Agent
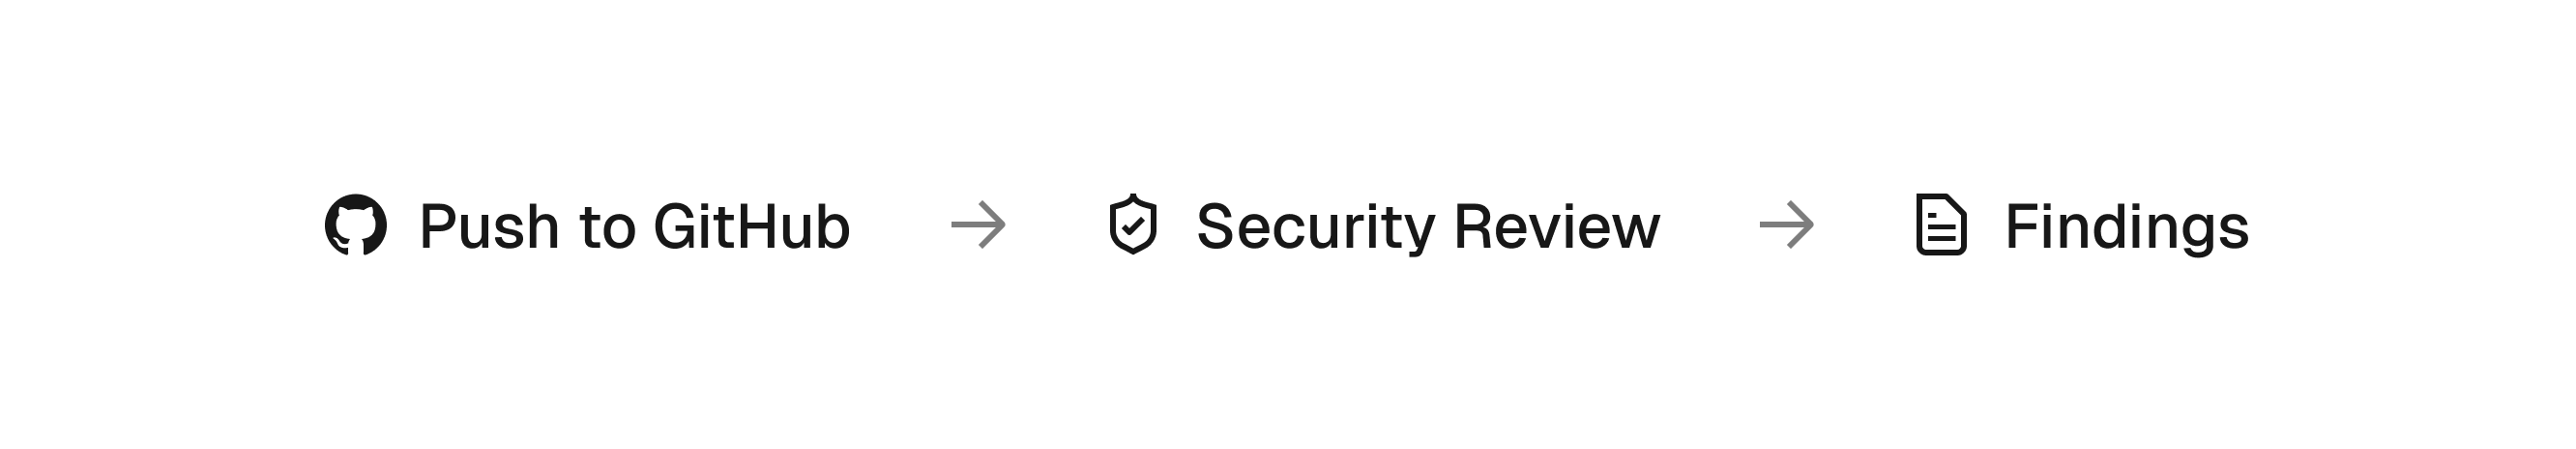
On November 3 (US Pacific time), Vercel launched Security Review in public beta. It is a new Vercel Agent capability alongside Code Review and Investigation: once enabled, every push to connected GitHub repositories triggers a diff-only vulnerability review that finishes in seconds. Findings land in the Security dashboard, PR comments and the CLI, and can be fixed with one click by Vercel Agent or pulled into your own coding agent via vercel security vulnerabilities. It is available to Pro and Enterprise teams, and reviews are free until November 10.
Key Takeaways
- Trigger: every GitHub push (including direct pushes to production) is reviewed automatically; only the diff is scanned, which Vercel says finishes in seconds, so it can run on every preview and production deployment
- Beyond pattern matching: the agent traces how changed code is reached, checks existing protections and rechecks each finding, which Vercel says catches logic flaws such as missing authorization checks
- Teams can write security policies in plain language, scoped to projects or the whole team, and manage them with
vercel security policy - Pricing: Vercel Agent rate, model tokens at provider cost with no markup, plus $0.25 per million tokens; reviews are free until November 10, 2026, while Agent fixes are billed
- Availability: public beta for Pro and Enterprise teams; Vercel has not published detection-rate or false-positive benchmarks
Linked Models & Agents: